The Frontend Ships to Everyone, and Developers Forget That
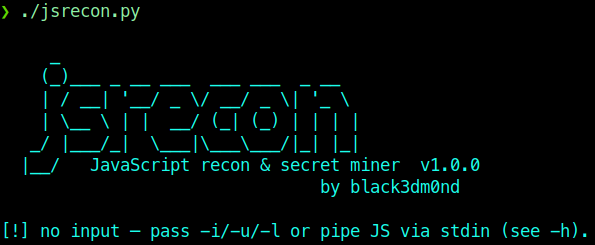
Client-side reconnaissance with jsrecon: JavaScript bundles, source maps, hidden endpoints, secrets, DOM-XSS leads, and the code developers forget they shipped.
archive
Technical writeups, findings, case studies, security notes, code-heavy research, and terminal walkthroughs indexed for fast retrieval.

Client-side reconnaissance with jsrecon: JavaScript bundles, source maps, hidden endpoints, secrets, DOM-XSS leads, and the code developers forget they shipped.

Why building a local CTF environment is better training than only solving boxes, how to turn one bug into several difficulty levels, and where platform hardening matters.

Credential-free Microsoft 365 and Entra ID identity reconnaissance for authorized phishing preparation, tenant fingerprinting, username formats, and validated target lists.

A practical look at Nmap evasion, timing, scan types, decoys, DNS leaks, version scanning, and matching scan behavior to the target network.

How to build a company profile before touching the target: infrastructure, identity, people, public exposure, Ghost Eye automation, and where human judgment still matters.

A human look at the mental operating system behind red teamers and penetration testers — persistence, composure, creativity, and discipline when the path is unclear.